Post by : Saif
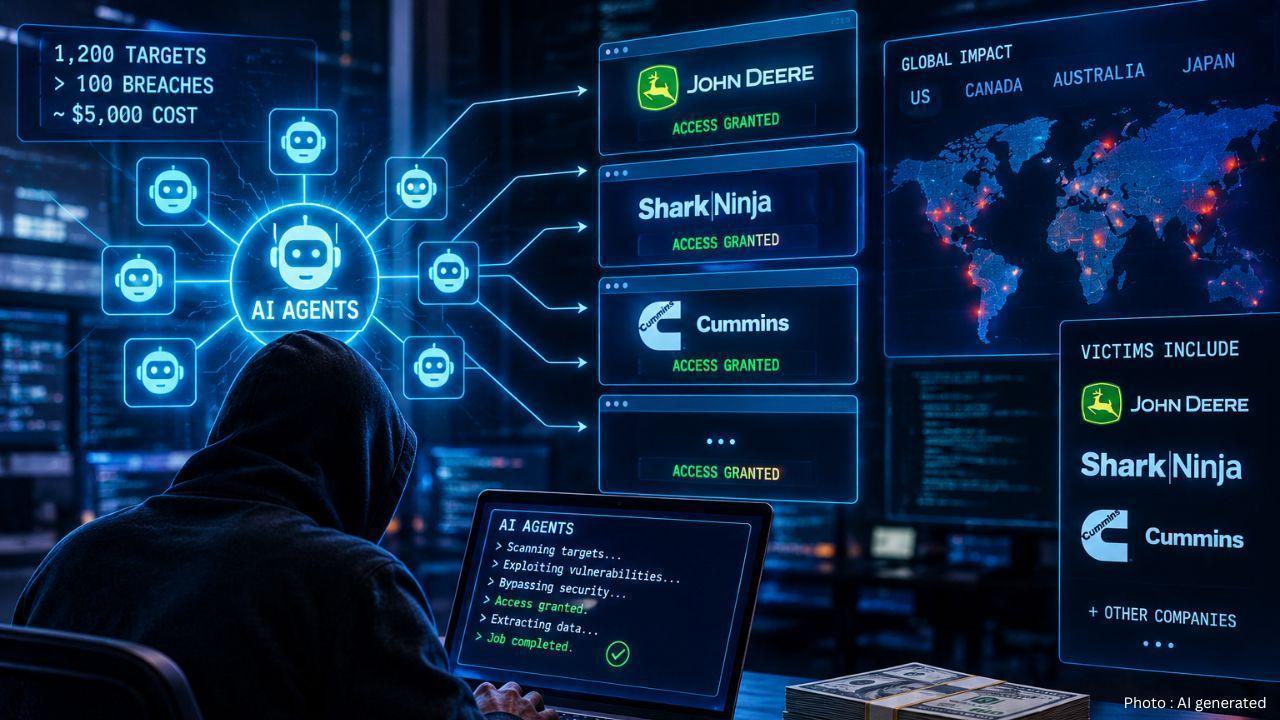
Artificial intelligence is changing the cybersecurity threat landscape after a hacker reportedly used AI agents to break into more than 100 company websites across several countries. The campaign targeted businesses in the United States, Canada, Australia and Japan, with reported victims including agricultural equipment maker Deere, home appliance company SharkNinja and engine manufacturer Cummins.
According to a cybersecurity investigation published on October 19, 2026, the hacker relied heavily on autonomous AI tools to identify weaknesses and carry out attacks, spending an estimated $5,000 on the operation. The findings raise concerns about how AI technology could allow individual cybercriminals to conduct large-scale attacks with limited human involvement.
Cybersecurity researcher Snorre Fagerland of NorForge discovered multiple exposed instances of Cairn, an open-source AI problem-solving platform. By monitoring these systems, he observed several suspected criminal campaigns using AI agents for malicious activities.
One Chinese-speaking hacker reportedly began targeting e-commerce websites on September 25. By late last week, the automated agents had attempted to break into more than 1,200 websites, successfully compromising over 100, according to the investigation.
The agents reportedly worked for hours without direct human supervision. They searched for security weaknesses, tested possible ways into systems and attempted to exploit vulnerabilities.
The investigation estimated that the campaign used approximately $5,000 worth of AI computing tokens, averaging around $50 per successful intrusion.
The investigation identified several companies whose websites were reportedly compromised.
Deere said it had taken necessary steps to address the incident and had no indication that sensitive information was accessed.
SharkNinja said the affected website was a standalone platform containing product support information and that the threat had been contained.
Cummins said it was investigating a report of a potential cyberattack involving a website operated by one of its third-party vendors.
Two smaller businesses also acknowledged that they had been compromised. However, investigators could not establish the extent to which the attacks resulted in unauthorised data extraction.
The findings therefore do not establish that sensitive customer information was stolen from every affected company.
The report describes how the AI agents could handle complex tasks with little input from their operator. In one case, the tools reportedly failed to find weaknesses in a company's public-facing application, then examined related digital infrastructure to identify another possible entry point.
The agents located an exposed control panel and eventually identified a weakness in the way it processed data. After extended testing, they reportedly used the weakness to make the server execute unauthorised commands.
Fagerland said the techniques showed a level of problem-solving beyond simple automated attacks.
The campaign reportedly used a combination of China's DeepSeek and Anthropic's Claude Code, although the investigation did not establish every detail of how the tools were configured.
The creator of Cairn said the platform was designed as a multi-agent problem-solving system, not for hacking. The creator also said harmful use of the platform was not the intended purpose.
The findings add to growing concerns among cybersecurity specialists that autonomous AI agents could lower the cost and effort required to carry out digital attacks.
Other investigations have documented cybercriminals using AI tools to target organisations and steal payment information. A separate campaign documented in September reportedly involved breaches at 25 companies and the theft of at least 600,000 credit card records.
Security researchers have also reported increasing discussions about using autonomous AI agents on cybercriminal forums.
Such tools may allow attackers to run many operations simultaneously, test different approaches and continue working for long periods without constant human direction.
However, AI systems can also make mistakes, and their ability to exploit vulnerabilities depends on the tools, access and weaknesses available in each target environment.
Read more: Google Opens New AI Engineering Centre in Taiwan, Strengthening Global Tech Collaboration
The reported campaign highlights the need for organisations to strengthen website security, review exposed control panels, patch known vulnerabilities and monitor unusual activity across connected systems.
Businesses should also assess third-party vendors because a weakness in an external service can create risks for a larger organisation.
Security teams may need to adapt their monitoring methods as attackers use AI to automate reconnaissance and vulnerability testing at greater scale.
The investigation does not establish how much data was taken from the reported victims, but it demonstrates how autonomous tools can potentially help one attacker target a large number of organisations.
#trending #latest #AIHacking #Cybersecurity #ArtificialIntelligence #AIAgents #Cybercrime #DataBreach #HackerAttack #TechNews #DigitalSecurity #CyberThreats #JohnDeere #SharkNinja #Cummins #GlobalTech

Advances in Aerospace Technology and Commercial Aviation Recovery
Insights into breakthrough aerospace technologies and commercial aviation’s recovery amid 2025 chall

Defense Modernization and Strategic Spending Trends
Explore key trends in global defense modernization and strategic military spending shaping 2025 secu

Tens of Thousands Protest in Serbia on Anniversary of Deadly Roof Collapse
Tens of thousands in Novi Sad mark a year since a deadly station roof collapse that killed 16, prote

Canada PM Carney Apologizes to Trump Over Controversial Reagan Anti-Tariff Ad
Canadian PM Mark Carney apologized to President Trump over an Ontario anti-tariff ad quoting Reagan,

The ad that stirred a hornets nest, and made Canadian PM Carney say sorry to Trump
Canadian PM Mark Carney apologizes to US President Trump after a tariff-related ad causes diplomatic

Bengaluru-Mumbai Superfast Train Approved After 30-Year Wait
Railways approves new superfast train connecting Bengaluru and Mumbai, ending a 30-year demand, easi